See code, dependency, and configuration risk in a single flow. Give your teams developer-friendly, fast, and measurable security operations.
Erbab.dev
AppSec Features
On every pull request
# Catch issues before they merge
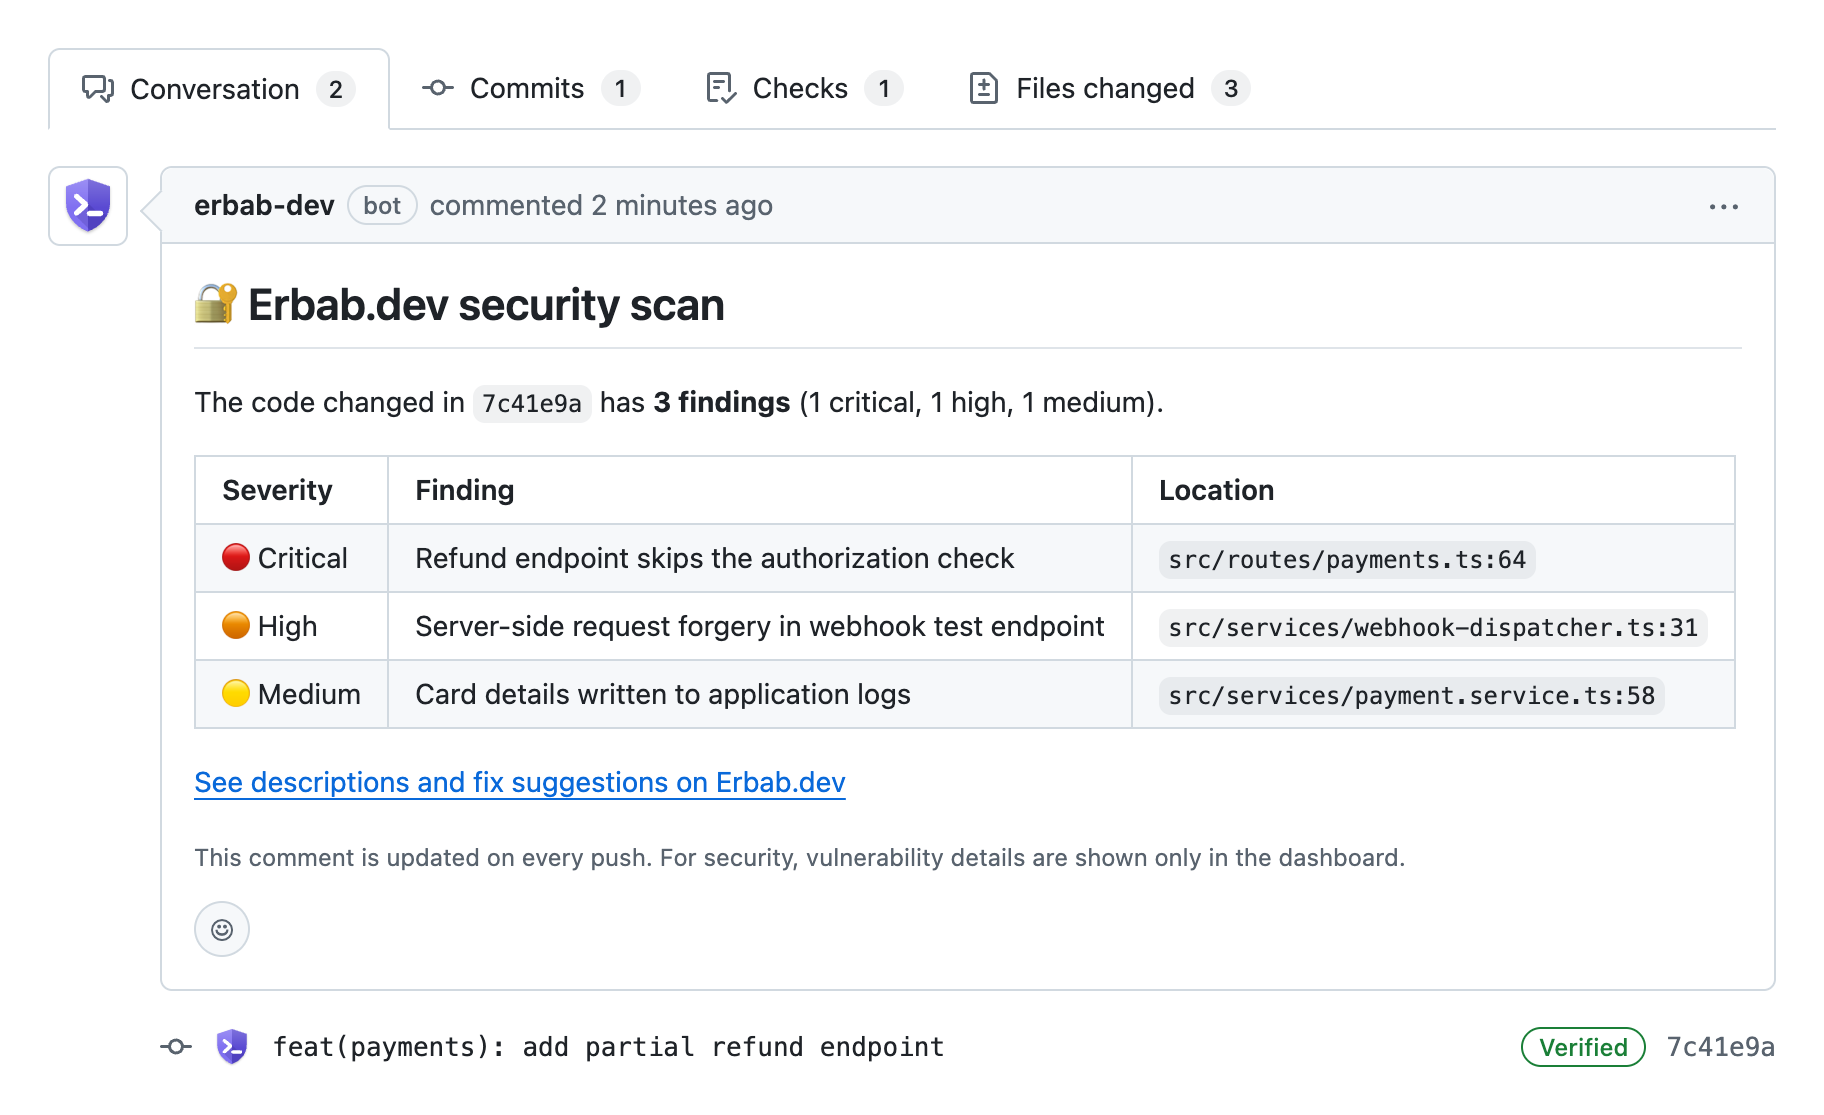
When a PR is opened or updated, only the changed code is scanned. The result is written to the PR as a single comment and a Check Run, and the same comment is updated on every push.
- If there is a critical or high finding the check fails, so you can block the merge
- PR comments only show a finding's name, severity and location; sensitive details stay in the dashboard
- Draft PRs are scanned once they are ready; PRs from forks are not scanned by default
Every month
# The whole repository, end to end
PR scans follow the change; the monthly full scan re-examines the entire codebase. Issues that build up over time, hide between two files or linger in old code don't slip through.
- An automatic full scan of every active repository each month
- Re-scan from the dashboard whenever you need to
- Comparison with the previous scan: new, fixed and still-open findings

Verification
# Verified findings, not noise
You don't have to dig through hundreds of alerts to find the real risk. Before it is reported, every finding is checked for whether it is actually exploitable, then ranked by severity.
- Clear prioritisation: critical, high, medium, low and info
- For every finding: why it's a problem, its possible impact and the evidence
- Mapped to OWASP Top 10 and CWE categories

Dashboard
# The whole picture on one screen
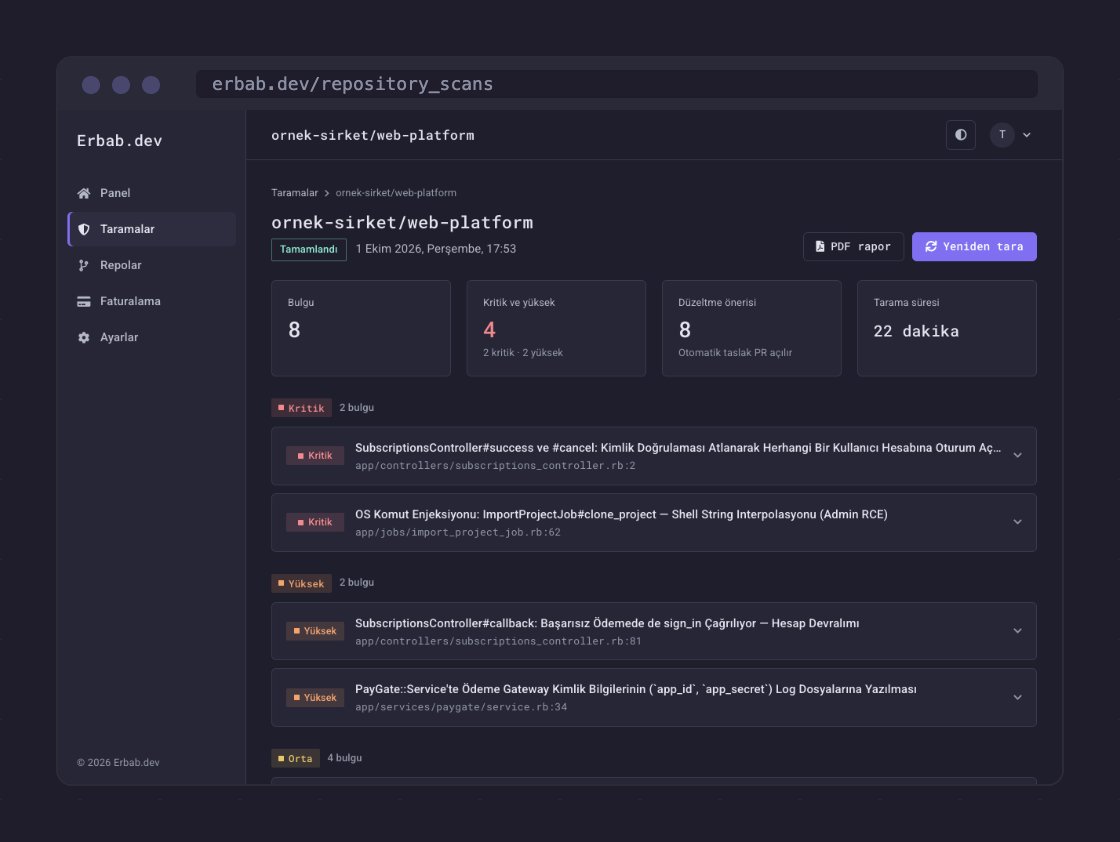
See the security posture of your repositories, the history of your scans and the details of every finding in one dashboard. No other tool is needed to track what was fixed and what is still open.
- Latest status and scan history per repository
- Explanation, impact, evidence and fix for every finding
- Light and dark themes with an easy-on-the-eyes design
Remediation
# The fix comes ready too
For verified, fixable findings the required change is prepared and opened in your repository as a draft pull request. Your team reviews it, runs the tests and merges when they're happy.
- Nothing is merged without your approval
- The PR description explains the problem and what the fix changes
- No duplicate PRs for the same finding

Reporting
# An audit-ready PDF report
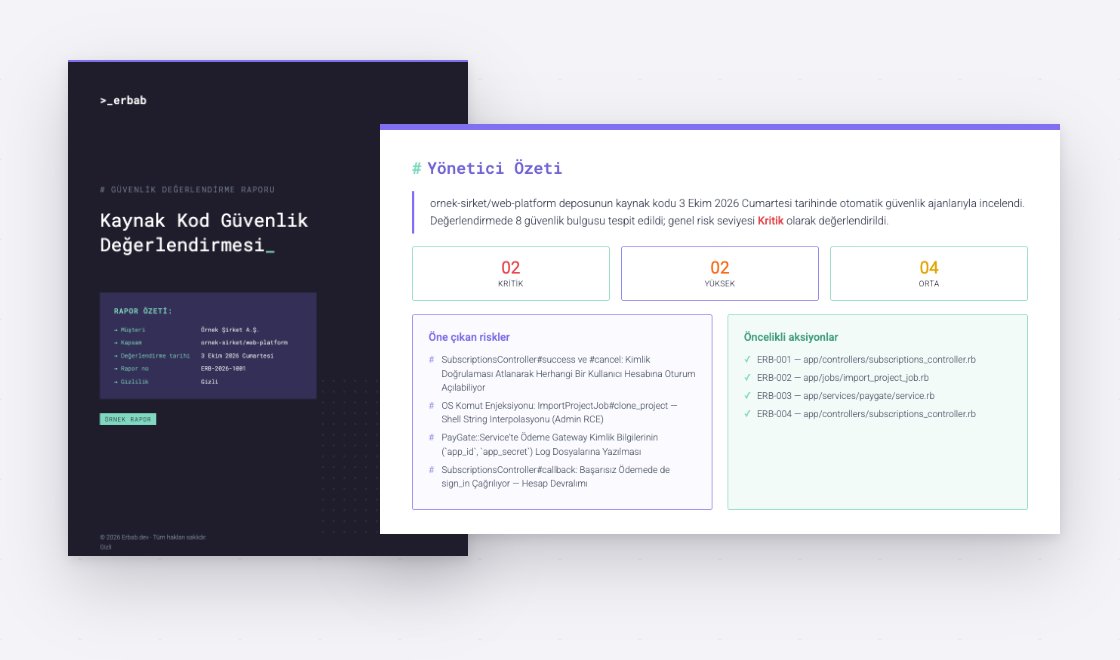
After every full scan a professional security report is prepared with an executive summary, a risk assessment, the scope and detailed findings, ready to share with your leadership, customers and auditors.
- OWASP Top 10, KVKK, ISO 27001 and PCI-DSS mappings
- Changes since the previous scan and fix status
- In English or Turkish
Trust
# Your code stays yours
A security product has to prove its own security first. Erbab.dev only processes your code for the duration of a scan, in an isolated environment created just for that scan.
- When the scan finishes the environment is deleted with all its data; no permanent copy is kept
- Your code is only used for your own scans
- GitHub access is limited to the repositories you choose and can be revoked with one click
- A self-hosted option on the Enterprise plan when your code must stay in your infrastructure